ISO 14001:2026 – An Opportunity for Change

Introduction

ISO 14001 is the most popular environmental management system standard in the world. There are over 1.2 million facilities certified to this globally recognized standard. Many other organizations are using ISO 14001 as a model for their EMS but have not yet sought certification. The revision of ISO 14001 in April of 2026 offers an opportunity for organizations with an older legacy EMS to review and update to better manage risk.

The ISO 14001:2026 update made no material changes to the basic requirements of the standard. The revision did, however, clarify some important requirements, especially in Clause 6 on Planning. The restructuring of this section helps organizations improve processes for environmental risk management. The restructuring also helps certification bodies and other auditors better understand what ISO intends for this clause of the standard.

Clause 6 is important because it determines what the environmental management system is going to manage (environmental aspects). Results of planning help everyone using the EMS understand what environmental risks are important to the organization. Planning also helps users of the EMS understand what actions the organization is taking to control environmental aspects and impacts.

Better Understanding of Environmental Aspect and Risk

Environmental aspects cause risk or environmental impact. Reducing risk of environmental impact is the primary outcome that an ISO 14001 EMS should achieve. Clause 6 on planning has been ambiguous about the relationship between risk(s), opportunities, aspects, and impacts. This leaves it up to the organizations to interpret the requirements when planning the EMS.

This ambiguity has led to a wide variety of approaches to identifying environmental aspects and determining which are significant. Although these approaches technically meet the requirements of ISO 14001 they are marginally effective in controlling risk from aspects. The ISO 14001:2026 revision helps users gain a better understanding of environmental aspects, impacts, risks and opportunities.

ISO 14001 requires that organizations identify significant environmental aspects and to address risk and opportunity associated with these environmental aspects. However, the standard provides little guidance on why organizations need to identify some environmental aspects as significant. The standard is also unclear about what to do differently with significant aspects than with those that are not significant. This approach allows organizations flexibility to meet the requirement of this part of the ISO 14001 standard. However, this flexibility has led to a wide range of approaches to identifying significant environmental aspects, impacts, risks, and opportunities.

Clause 6 From an Auditors Perspective

Some conformant legacy EMS processes identify only a few environmental aspects and only 1 that is significant. Others are complex Failure Mode Effects Analysis (FMEA) type methods. Some with 7 or more factors used to calculate a Risk Priority Number (RPN). Often the FMEA has an arbitrary RPN cutoff value that limits the number of significant aspects.

Although these approaches met the basic requirements of ISO 14001, they often did not help organizations identify what was important. If the planning part of the EMS is weak the rest of the management system suffers. This is because the rest of the EMS relies heavily on the output of clause 6 planning.

ISO 14001:2026 revisions in clause 6 used a three bucket concept. The standard reordered the sequent of clauses to focuses on environmental aspects as a priority (Bucket-1). Bucket 2 are compliance obligations and Bucket 3 are risk and opportunities. See Figure 1.
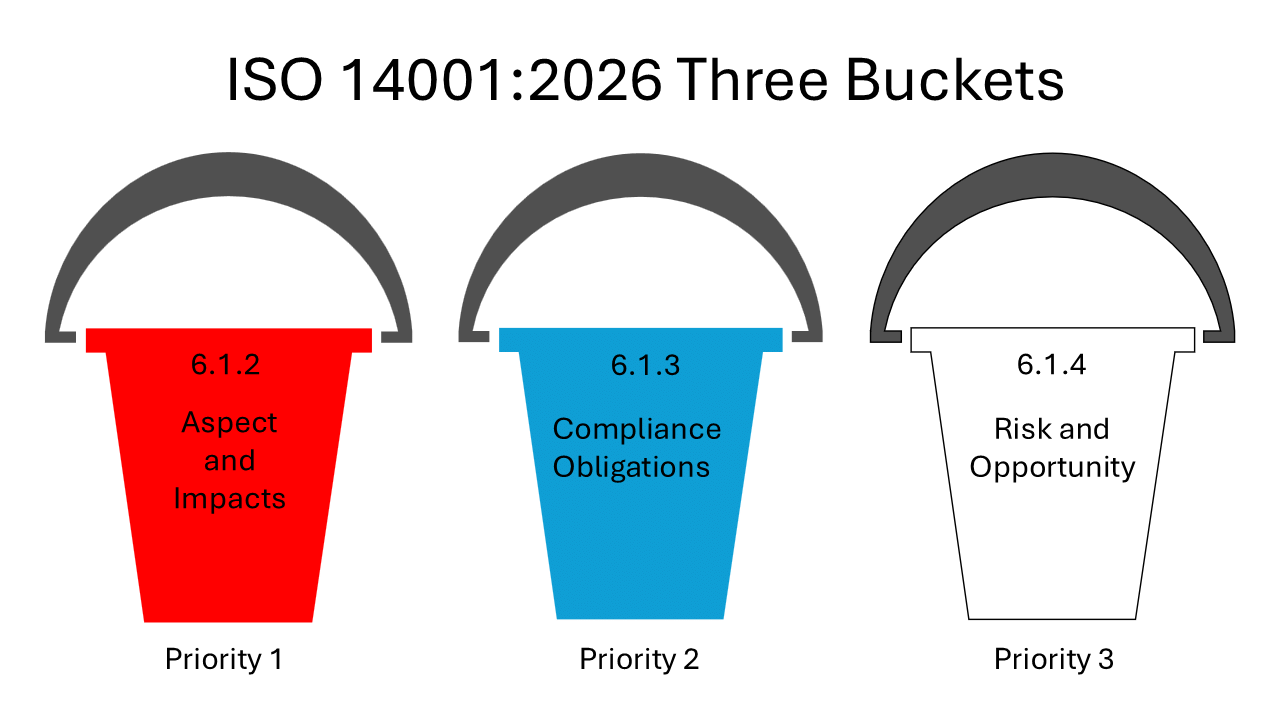
Figure 1 – Three Bucket Concept

The following example of cheese making illustrates one approach to identify environmental aspects, impacts, determine which are significant. The case study describes how organizations can determine actions needed to address environmental risk and opportunities. It also provides information on how the ISO 14001:2026 EMS planning supports other parts of the EMS including auditing.

Process Flow Diagrams Aid Aspect Identification

Most organizations have systematic processes that add value and help organizations generate revenue. Often these processes have environmental aspects and impacts. Mapping the process flow is the first step in identifying environmental aspects. In manufacturing, businesses use inputs, like raw materials and energy in a sequence of processes that change these raw materials into something with more value that the organization can sell to customers.

Developing a process flow diagram of the manufacturing process is a critical step in aspect identification. Figure 2 is an example of a cheese making process flow diagram.   Raw milk is one of the inputs into the process. The cheese making process changes milk into cheese through a sequence of steps. The result of the process in cheese ready for sale to customers.
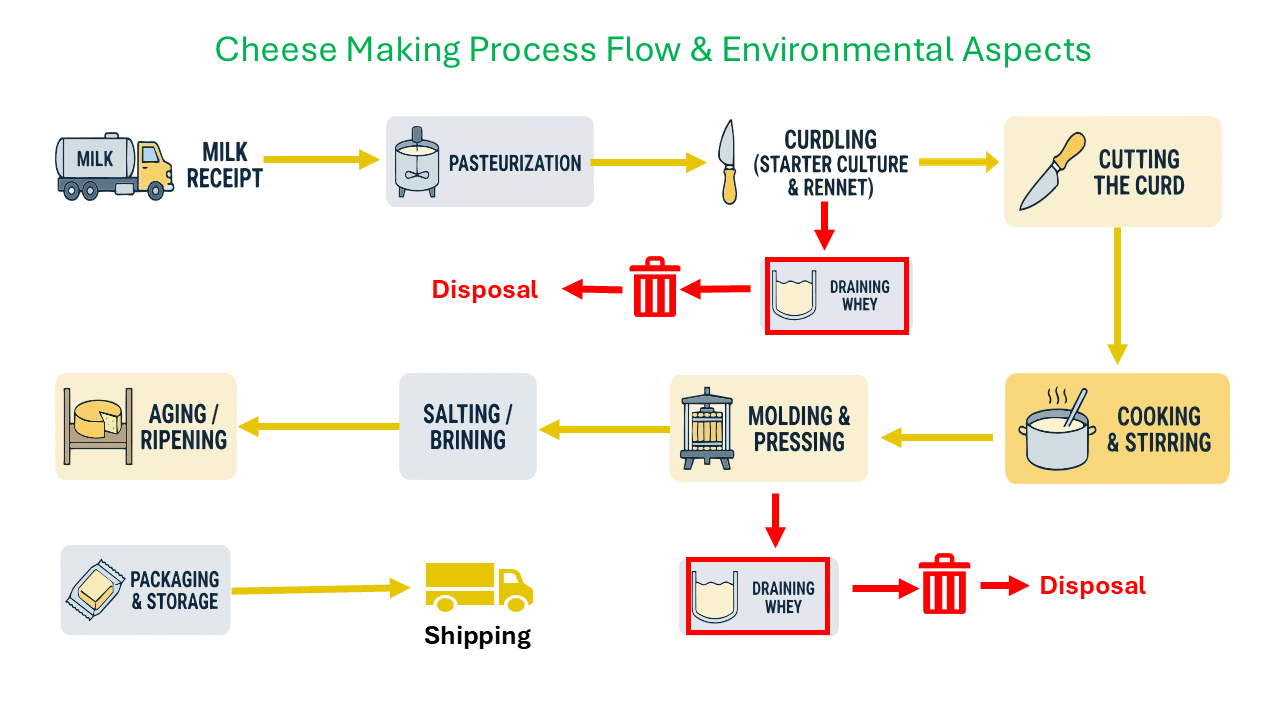
Figure 2 – Cheese Manufacturing – Whey Environmental Aspect

Waste whey is an output of the curdling and molding processes. If mismanaged it can have a significant water pollution environmental impact. To avoid fines and damage to the company’s brand risk of noncompliance from mismanagement of waste whey should be addressed by the company

The cheese making process has many other environmental aspects that may be significant like the use of cleaning chemicals and potential emissions of pollutants into the air. The first step in the Clause 6 planning process is to create an inventory of environmental aspects.

Use a process flow diagram like the one in figure 1 to identify environmental aspects.   Include someone with knowledge of environmental impacts are for the cheese making process. Once you have an inventory you can begin to evaluate them for importance using risk assessment techniques.

Deciding What Is Important

ISO 14001 requires organization’s determine what environmental aspects are important (significant) and thereby need to be addressed.

“The organization shall determine those aspects that have or can have a significant environmental impact (i.e. significant environmental aspects) by using established criteria.”

Risk assessment should be used to determine which environmental aspects are important and need to be controlled or improved. However, risk assessment can be subjective and imprecise. There are many approaches to performing risk assessment. The key is to not make it overly complicated. Keep it simple.

Figure 3 is an example of a simple risk matrix you can use to estimate relative risk based on likelihood and severity.
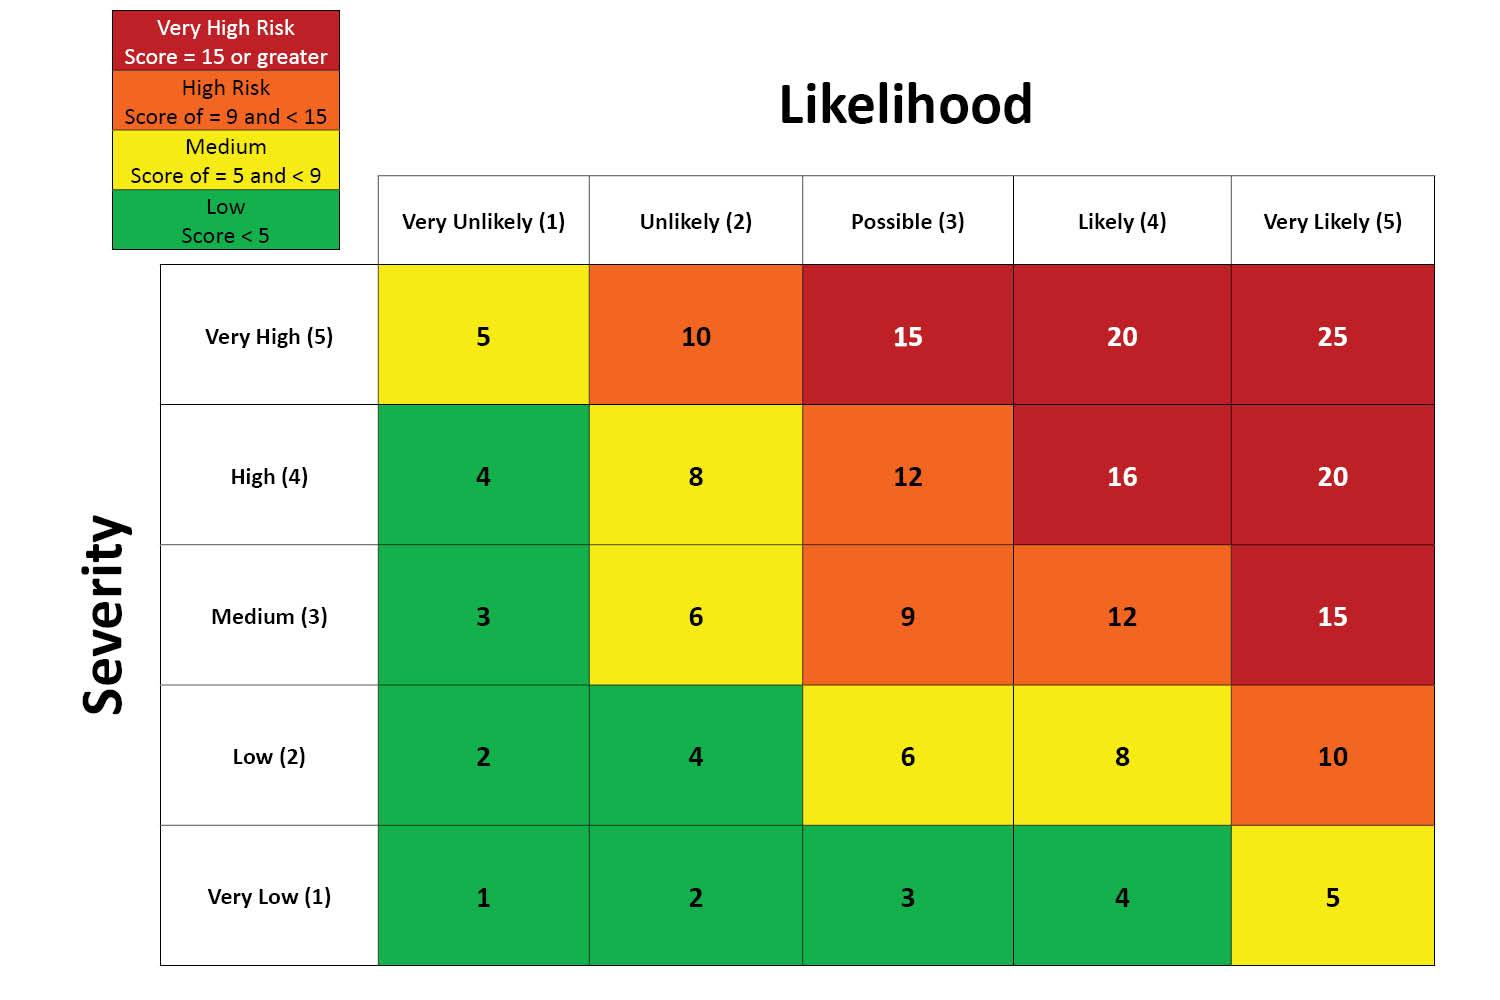
Figure 3 – 5×5 Risk Analysis Matrix – CorrectTrack.com

Across the top of the matrix are values for the likelihood that an aspect will have an impact on the environment.  The likelihood values in the top row increase from left to right, not likely (Value of 1) to Very likely with a (value of 5).  The Severity values along the left side of the matrix are similar with Low (1) at the bottom and Very High (5) at the top.

Use the matrix to estimate risk. Start by assuming that there are no existing controls to manage the risk of environmental impact even if you do have exiting controls in place. Pick a value along the Severity axis that you think is reasonable (1-5). Then pick a value along the Likelihood axis that you think is reasonable using the 1-5 scale. Multiply these 2 values together to give the estimated risk value. A group is often better at estimating these values than one individual alone. Also include an environmental professional with some risk assessment experience to guide the risk assessment process.

Significant Environmental Aspects

When making cheese, enzymes are added to the milk to help the milk coagulate into cheeses curds.  The enzymes come in returnable containers, and the likelihood is low and severity of an impact from adding enzyme is low. The risk score is calculated by multiplying the likelihood times the severity which gives a risk value of 1 which is low and represented by the color green on the matrix.

The generation of waste whey from the milk curdling process is highly likely (5) on the matrix because it happens every day that cheese is being made. The impact of improper disposal of waste whey is either high (4) or very high also (5). The combined estimated risk is calculated to be either 15 or 25 (high or very high) color red. This uncontrolled risk score helps in prioritizing environmental aspects for risk control   Figure 4 is an example of a prioritized aspect list.
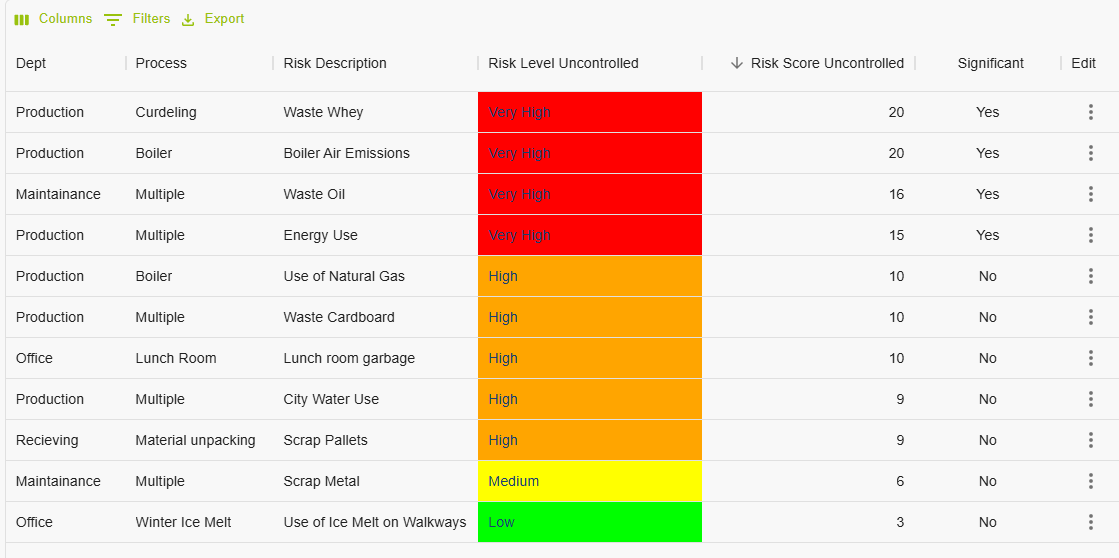
Figure 4 – Prioritized Aspect List for Cheese Making

Good Planning Equals Good Audits

Skillful planning helps ensure good audits. Good audits provide critical information to leadership and others about the performance of the EMS and its ability to control risk to the organization. A well-planned EMS links environmental risk to the controls established to address the risk. This linkage is like a breadcrumb auditors can follow to check that the environmental risk is being addressed and the control is effective.

Breadcrumbs for Audits

A good example is Used Oil Management. Some of the equipment in the cheese factory is lubricated with petroleum oil. This oil needs to be changed by the maintenance department from time to time to protect the equipment moving parts from excessive wear. Without adequate controls used oil can be mismanaged and dumped on the ground, in sewers and storm drains causing significant environmental impact.

The likelihood and severity of environmental impact is high if used oil is mismanaged. Used oil is also regulated by government agencies and organizations and its leadership risk fines and even criminal penalties if waste oil is mismanaged.

To ensure that risk from the aspect of used oil is minimized organizations can establish several controls including Spill Prevention Control and Countermeasures Plans, secondary containment of used oil drums and tanks, and documented work instructions. By connecting the environmental aspect of used oil to these controls the auditor can quickly confirm what controls need to be in place and if those controls are effective. Audits would check that the SPCC Plan and the used oil work instructions are being followed.

Hierarchy of Control (HOC)

EMS Planning includes consideration of what actions can control environmental risk. Risk controls take several different forms, and not all are equally effective.  One method for determining the effectiveness of risk control is the Hierarchy of Controls (HOC).  HOC is based on the concept that some types of control are more effective at reducing risk than others. In the HOC “Elimination” is one of the methods to control risk.

If a cheese factory is able to eliminate the process that generates the whey waste the risk of that aspect is also eliminated and the risk score goes from 25 to 0. Figure 5 is a version of the HOC used to calculate the effectiveness of a particular type of operational control Engineering controls reduce risk by 60% and administrative controls by 40% and so on.
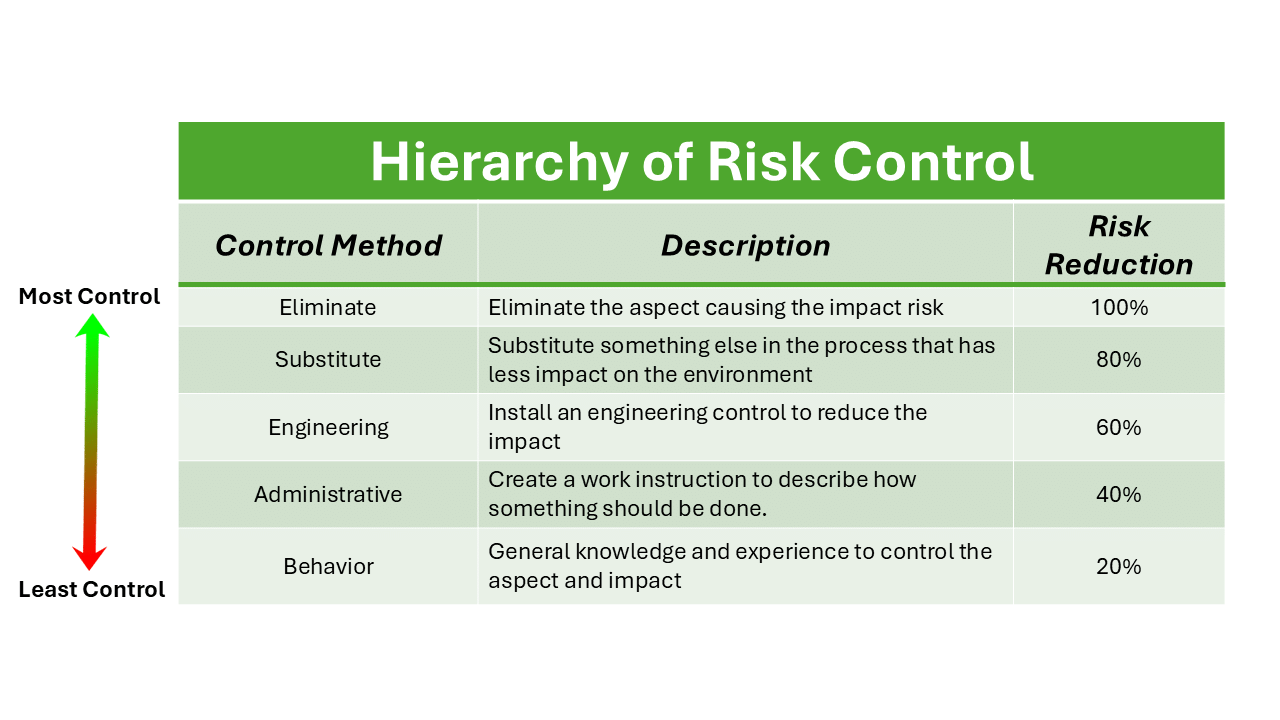
Figure 5 – Hierarchy of Risk Control – CorrectTrack

Layers of Protection (LOP)

Another important concept of risk control is Layers of Protection. If we apply several different controls to the aspect of Waste Whey we can reduce risk from this aspect significantly.The calculated uncontrolled risk score for waste whey at 25 (Very High). We can use an engineering control (treat the wastewater before discharge). This will reduce that risk score by 60% down from 20 to 8 (20 x .4=8). This reduced value is the residual or remaining risk before any additional control.

A risk value of 8 for the aspect is still high (orange). Another layer of protection is desirable to reduce the risk further. The organization needs to be maintain the wastewater treatment process. Leadership should confirm that treatment plant operators are competent to ensure the treatment is done properly. Training and competence are a form of administrative operational control in the Hierarchy of Control (See Figure 3).

Appetite for Risk

This additional layer of protection reduces the risidual risk to 4.8. Depending on the organization’s appetites for risk, this value may be low enough. Leadership should review and confirm risk to the organization is managed adequately. Repeating this process for all other environmental aspects ensures that risk is assessed and addressed to an acceptable level.

Tying It Altogether

The ISO 14001:2026 revision emphasized the importance of clause 6 and good planning. The intent is to encourage organizations to review their planning process. Organizations with a legacy EMS will benefit from reviewing the planning parts of their EMS. Important questions to ask during this review are:

  • Was a process flow diagram or something similar consulted during the aspect identification process?
  • Are risk assessment processes used based on likelihood and severity of impact?
  • Were aspects with higher risk values prioritized for action?
  • Does the risk assessment process consider the hierarchy of controls when deciding if risk had been adequately addressed?
  • Has linkage between the environmental aspects and the actions taken to control risk been documented?

Answering yes means the planning part meets the requirements of ISO 14001:2026 and is addressing environmental risk. If not maybe now is a good time to make some changes to the planning process.

About the Author:

Kevin Lehner is a senior member of the ANSI US technical Advisory Groups for ISO 14001, 45001 and ANSI Z10.  He is leading the international group establishing a new guidance standard in the ISO 14002 series on using ISO 14001 to address environmental topic areas.  He is a certified ISO management systems lead auditor performing frequent ISO audits for ECSI audit clients.  He also is a frequent instructor for ISO 14001, 9001 and 45001, auditor and lead auditor Exemplar Global certified courses.

Understanding Green Tier Audits

The Wisconsin Department of Natural Resources Green Tier program has requirements for participants to perform different types of audits of their Environmental Management Systems (EMS). Understanding these types of audits and who can perform them will help ensure compliance with Green Tier. The types of Green Tier audits are:

  • EMS Internal audits
  • EMS Outside Audits
  • Regulatory Compliance Audits

Types of Audits and Frequency

EMS Internal Audits

Internal audits can be performed by the participant themselves or by independent auditors. These audits are then used as part of the management review process to help leadership evaluate the performance of the EMS and to decide if any changes are needed to improve it. They must be documented, performed at least annually and conducted by competent objective auditors.

Outside Audits

Outside audits are performed by independent auditors that have been approved by WDNR to perform these audits. Tier 1 participants must perform these audit at least every 3 years. Tier 2 participants need to have an WDNR approved auditor perform these audits at least annually.

Compliance Audits

Compliance audits are different than the Outside Audit described above. These audits check that the organization is meeting the USEPA, WDNR and local legal requirements. These include requirements for emitting pollutants to the atmosphere, water, solid and hazardous waste disposal. Tier 2 participants need to perform compliance audits at least annually and report the results to WDNR. These audits can be internal audits or performed by other independent auditors.

Why Does Green Tier Require Audits?

The Green Tier Law is based on the requirements of ISO 14001 which also requires periodic audits of the EMS. ISO 14001 is itself based on the principals of continual improvement (PDCA). Audits are the checking part of the PDCA cycle.

Who is Qualified to Perfrom External Audits

Only WDNR approved Green Tier auditors are qualified to perform external audits. Green Tier participants should confirm that their auditor is on this approved list. Participants should do this even if they are using an ANAB accredited ISO 14001 certification body to perform their external audits. If you have any questions about Green Tier audits, who is qualified to do audits or want to know how to get the most out of your audit contact us for at kalehner@envcompsys.com or use the form below.

Contact Form

URGENT ALERT – ISO Climate Change Amendments!

ISO recently amended all ISO management system standards (MSS) to include requirements for organizations to consider the effects of climate change. If your organization holds a current certification to ISO 9001, 14001 or 45001 you can expect to be asked “has your organization determined whether climate change is a relevant issue?” during your next certification audit.

This new requirement is the result of a change to the ISO Harmonized Structure (Appendix 2 of the Annex SL in the ISO/IEC Directives Part 1 Consolidated ISO Supplement). Here is more background on the Harmonized Structure also referred to as the High Level Structure and Annex SL.

ISO announced the new requirement in an IAF/ISO Joint Communique indicating the climate change text highlighted below is effective immediately for all MSS.

ISO HLS revised requirements for context determination

Most organizations certified to ISO 14001 should be able to answer auditors questions about climate change relevance. Other organizations with current certification to ISO 9001 and/or 45001 might find it more difficult to avoid a nonconformity to these new requirements if they don’t act soon. Each organizations context is different and will influence how they address climate change in their MSS

Contact us if you have questions about how these new requirements might effect your organization ISO certification status.

New Sustainability Information Verification and Validation Protocol

Corporate Sustainability Reporting (CSR) began over 25 years ago with the Global Report Initiative (GRI).  Since then, use of CSR information by investors and potential customers has increased.  Unlike financial reporting, the accuracy and truthfulness of sustainability information has been mostly unregulated leading to abundant misstatements aka, greenwash in CSR and other sustainability reports. Stakeholders, including investors, customers and others are increasingly requesting robust qualitative and quantitative sustainability data and information to base their economic decisions on. These stakeholders are looking for assurance from competent providers to help them confirm the information they are using is true. Assurance service providers now have several protocol they can follow when verifying sustainability information.

The following is a brief description of some of the protocol being developed to perform assurance of sustainability information.

ISO 14019 Series – Validation and Verification of Sustainability Information

ISO is developing standards in the ISO 14019 series titled Validation and Verification of Sustainability Information. This series is designed to cover all types of sustainability information including Environmental, Social and Governance (ESG). Green house gas emission information is one example of the types of information these standards will cover. Other types of information will include information and claims about:

  • amount of waste sent to a landfill,
  • water the organizations uses and discharges as waste water.
  • emission of other toxic pollutant to the atmosphere,
  • assertions about occupational health and safety performance.

The series will include:

14019-1   General principles and requirements for validation and verification
14019-2   Principles and requirements for verification processes
14019-3   Principles and requirements for validation processes
14019-4   Principles and requirements for bodies validating and verifying sustainability information.

The United States Security and Exchange Commission (SEC)

Recently the SEC  took action against organizations using misleading sustainability information to market their financial products.  SEC is also enhancing its authority to further regulate misstatements with issuance of the long anticipated Climate Disclosure Rule.  The SEC climate disclosure rule issued now include requiring  verification of GHG information by an independent verification service provider.  

International Audit and Assurance Standards Board (IAASB)

IAASB is also about to issue standards that will cover assurance of all types of sustainability information. ISSA 5000 is titled General Requirements for Sustainability Assurance Engagements. This protocol will likely be preferred by Certified Public Account firms because this protocell has been developed largely by the financial accounting profession.

What’s Next?

There are many questions about which if any of these new verification standards will be broadly accepted and by whom.  ISO 14019 series may be more acceptable to non-CPAs including sustainability consultants.  Other questions include who, if anyone will accredit the assurance bodies. This field of practice is developing quickly so stay tuned. We should have answers to these questions soon. If you have any questions contact us here.

Kevin Lehner is the Chair of the US Technical Advisory Group Sub TAG that is developing the ISO 14019 series.  He is also the Vice Chair of the US Technical Advisory Group to TC 283 and represents the American National Standards Group international for the development of ISO 45000 series of standards on occupational health and safety.  His practice includes performing certification audits, training auditors and help organizations integrate ISO 14001 and 45001 into their other business management systems.

Pro Tips for Best EHS Audits (Part 3): EHS Audit Follow-up

The purpose of an EHS audit follow-up is to check that EHS risk, including risk of noncompliance, is managed to a level that the organization considers acceptable. Noncompliance with applicable government laws and other requirements are examples of EHS risk sources that need to be controlled. An EHS audit checks that risk controls are in place and effective.  Risk controls can be engineering controls like air pollution control devices, administrative controls like training and work instructions and others.

EHS Audit Findings

The results of an audit are called findings. These can either be positive findings that the controls are in place and effective, or negative. Negative findings are nonconformance’s. Positive findings are good news but not something the organization needs to act on. Positive findings confirm that “what should be is” and that “what should not be is not.

Negative findings however are actionable and create opportunities to improve EHS performance. In Part 2 of this EHS Compliance Audit series, we discussed how negative findings are written and communicated verbally at the end of the audit. As a follow-up to the active evidence gathering and verbal reporting, a written report should be prepared and distributed to document the results of the audit.

Preparing the EHS Audit Follow-Up Report

The audit report presents the results to the auditee and others and helps an organization gauge EHS performance. The report should be concise and to the point and the tone of the report should be factual and nonjudgmental.   

A key part of the EHS audit follow-up report are the negative findings that were made during the audit. The EHS audit follow-up report formalizes the findings in a way that the auditee can act on them. The reported negative findings need to include enough information so that they can be investigated and ultimately fixed in a way that they do not happen again.

Here is an example outline for an EHS audit follow-up report.

  • Executive Summary
  • Background Purpose and Scope
  • Findings
  • Conclusions
  • Recommendations
  • Discussion
  • Appendices

Correction and Corrective Action

Negative EHS audit findings point to EHS risks that need to be better controlled. They are the result of a potential noncompliance with a legal requirement or discovery of some other issue. If left uncorrected they can increase risk and lead to enhanced legal action by a regulatory agency (knowing and willful violation). To avoid exposure to these enhanced penalties, it is important that organizations have a good corrective action process in place.

There are 5 steps in an effective corrective action processes.

  1. Short Term Correction
  2. Investigate the Cause
  3. Identify a Corrective Action
  4. Implement the Corrective Action
  5. Verify the Corrective Action is Effective

The following is a brief description of these steps.

Short Term Correction

Findings that identify a potential serious risk need to be addressed as soon as possible. Continuing to operate equipment that exposes workers to injury after a finding is made is bad business. If a worker were to become injured after the nonconformance was reported the penalties and fines could escalate dramatically.  A correction to quickly reduce the risk from the nonconformance needs to be put in place as soon as practical.

Investigate THE Cause

Once the correction has been put in place a corrective action plan needs to be established. Responsibility to investigate the cause of an audit finding should be assigned to someone with knowledge of and experience with the corrective action process. This knowledge and experience will help identify the root cause of the finding. Once the root cause is established an appropriate corrective action can be proposed that prevents the problem from recurring in the future.

Knowledge and use of root cause analysis tools like “5 Why Cause Analysis” ensure the cause of the unacceptable risk level is identified. Here is an example a “5 Why Cause Analysis”.

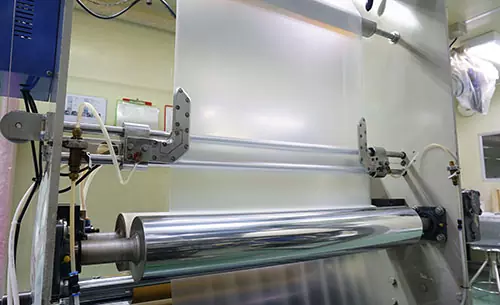
This example is for an incident that happened at a roll calendar for polishing extruded plastics sheets. An employee was caught in an in running nip between the rolls and luckily only sustained a recordable injury. This incident could have easily been an amputation or a fatality.

roll calendar for polishing extruded plastics sheets
Why?Answer
Why was the OHS hazard of being caught in the nip on the calendar not addressed?The machine was new, and no one thought to do a Job Safety Analysis (JSA) before it was installed and operated.
Why did no one perform a JSA?Performing a JSA to review potential OHS hazards and risk are not part of the capital investment approval process.
Why was OHS hazard and risk review not part of the capital investment process?The manager of the extrusion department manager did not know that a JSA hazard and risk review should be undertaken for all new equipment as part of the purchase process.
Why was extrusion department manager unaware of the need to review hazards and risks for new equipment?An existing employee had recently been promoted to manager of the extrusion department and they had not been informed of the requirement.
Why had the new extrusion department manager not been informed?Our organization has not established a process to identify training needs and provide training to employees when they transfer to a new position within the company.
Table 1 – Example 5 why analysis

Identify a Corrective Action

Once the cause is established, a suitable corrective action can be identified to reduce the risk to an acceptable level. The effort needed to identify a suitable corrective action is proportional to the finding risk level. The higher the risk, the more effort needed to figure out the best way to address it. A finding that an emergency evacuation map could be hidden behind a door when it is opened, is much easier to correct than the finding of an ineffective control to treat wastewater discharge to a municipal sanitary sewer.  

The cause analysis process should have an approval step to confirm the cause analysis was performed with skill and that the corrective action is aligned with the identified cause of the finding. This review and approval can be done by the auditor who made the finding or others in the organization who can impartially review the cause and proposed corrective action.

If the cause and/or the proposed corrective action are found to be deficient during the review, the assignees should be consulted and asked to rethink the cause analysis and corrective action. The evaluation and approval of potential corrective actions requires striking a balance between risk and opportunity. It is not possible to reduce all risk levels to zero.

Some processes have hazards with risk that are difficult to control and the organization needs to think carefully about what level of risk it is willing to accept. In running nips on plastic extrusion rollers is a good example. It is very difficult to properly guard an in running nip on these machines. The guard would prevent the process from working properly.

As a result, the corrective action cannot be the elimination of the hazard or installation of a physical guard (engineering control).  Instead, there may need to be several independent controls such as installing a rope e-stop, providing training to employees on how to operate the process safely and even evaluating the operators competence to ensure they understand the hazard and the associated risk. 

Once both the cause and the corrective action(s) are approved the assignee should be authorized to implement the corrective action.

Implement the Corrective Action

The implementation of the chosen corrective action may take days, weeks or even months depending on what needs to be done. Moving an emergency evacuation sign to a better location can be done almost immediately while designing and installing an upgraded wastewater treatment process may take many months.

Verify the Corrective Action is Effective

Verification that the corrective action has been implemented and that it is effective is the last step in the process. It confirms that the problem causing risk, has reduced that risk. The verification can be done upon completion of the corrective action or during the next audit. When the corrective action is verified, it can be closed.

Tracking EHS Audit Corrective Action Progress

Historically, keeping track of progress toward completing corrective action was done with paper forms that went from in-basket to in-basket. Once complete they were placed in a file drawer for storage. Later, electronic methods including excel spreadsheets and other types of electronic documents were used with some success. However, these tracking methods require much effort and often lead to miscommunications or missed deadlines of incomplete corrective actions for findings. The result was the corrective action process was not successful in reducing risk in a timely fashion and increased risk to the organization. 

Within the last few years cloud-based applications have emerged that solved many of the problems with paper or spreadsheet corrective action tracking systems. These applications allow quick access to users and are readily accessible almost anywhere.

Modern corrective action application
Figure 1 – Modern Corrective Action Application

Cloud based database applications help organizations quickly find the status of any CA and drill down to details for each CA.

Figure 2 – Drill Down Corrective Actions Detail

Applications like CorrectTrack establish users permissions to view, change, verify and approve corrective actions. A permissions based peer review process also helps ensure that corrective actions are investigated thoroughly and verified before they are closed.

Other advantages of a cloud based app like CorrectTrack are:

  • Notify persons of status changes of a CA
  • Define a standard process for doing CA
  • At a glance dashboards for users
  • Provide notifications when CAs are coming due, or past due
  • Provide a record of who changed what, when and why
  • User permissions allow visibility of the CA system to leadership

Conclusion

Effective corrective action processes are powerful tools that help organizations improve EHS performance over time. Investing in, and continually improving the corrective action process will provide a significant short term and long term return.

This EHS Audit Follow-up post is part 3 of a three part article on EHS Auditing. Part 1 and 2 discussed how to plan an EHS audit and conduct an EHS audit. This concludes our three-part series on EHS audits.

We welcome and encourage feedback on this series. Contact us directly at kalehner@envcompsys.com and 262-949-2965, or visit us online for more information: ECSI or CorrectTrack.

Pro-Tips for Best EHS Audits (Part 2): Conducting an EHS Compliance Audit

Compliance audits confirm an organization’s compliance status with environmental and occupational health and safety regulations. Audits also help manage risk of violations and fines. Customers, boards of directors and others care about EHS regulatory compliance and use audit results to make important business decisions. EHS audits will become even more important in the future as more organizations seek independent verification of their EHS and ESG performance.

Opening Meeting 

An EHS compliance audit can be intimidating for an organization. Conducting an opening meeting helps to: 

  • Explain the purpose, scope, and objective(s) of the audit.
  • Introduce the audit team, the auditee leadership and audit participants. 
  • Present the audit schedule.
  • Discuss who has authorized the performance of the audit and why.
  • Describe how evidence will be collected during the audit.
  • Review how audit results will be reported.

Participation of leadership at the opening meeting helps communicate support for the audit process and expectations for employee participation in the audit.

Collecting EHS Compliance Audit Evidence 

In Part 1 of this series, we discussed how to plan an EHS compliance audit focusing on what matters (materiality).  Auditors use the audit plan to develop audit trails that result in positive or negative evidence of compliance. A questions like “tell me about the processes operated in this department” is often a good starting point for developing audit trails. Here is an example follow-up questions an auditor could ask to further develop the compliance audit trails. 

Auditor: I see the metal parts grit blast process is operating today. What kind of parts are you blasting now.

Auditee: We are cleaning several hundred parts before they are electroplated.

Auditor: What are some of the important environmental aspects and OHS hazards you need to consider when operating the grit blaster and dust collector when cleaning stainless steel parts?

A well-prepared auditee will have identified the environmental and occupational health and safety regulations before the audit. Figure 1 is an example of a risk analysis tool that helps prepare for an audit and helps auditors identify important areas to audit. For more information about risk analysis watch this Risk Overview brief video.  Learn more about CorrectTrack app.

EHS risk analysis tool
Figure 1- EHS risk analysis tool

Tools like CorrectTrack provide a listing of environmental aspects and OHS hazards. The list helps quickly identify important aspects and hazards that are good candidates for improvement or for developing audit trails.  The highlighted row in Figure 1 is an example of an environmental aspect to check during an audit.  Clicking on Risk ID 803 link shows the risk detail page (Figure 2).

Grit Blast Dust Emission Environmental Risk Detail
Figure 2 – Grit Blast Dust Emission Environmental Risk Detail

This page shows important details about a dust emissions risk and provides links to other information like risk controls, applicable compliance obligations and related files. Clicking on the link under “Files” provides more detailed information (Figure 3). The red box in Figure 3 shows the specific requirements (risks) that need to be addressed or that are (audit criteria) an auditor can check.

Air Permit Audit Criteria for Dust Collector
Figure 3 – Air Permit Audit Criteria for Dust Collector

Collecting And Evaluating Evidence 

An audit checklist can help jog an auditor’s memory of the audit trails they want to follow. Checklists can be as needed. A good checklist points the auditor to what they are trying to prove true.  It should be more than a simple check the box yes or no checklist. Check the box checklists discourage looking for and recording evidence of conformity of compliance and should be avoided

The best checklists are prepared by the auditor before or during the onsite portion of the audit. They are specific to the process being audited and the requirement being assessed. The line of questioning can be spontaneous and not always needs to be documented. The questions can be recorded on the spot in the auditors notes along with any evidence observed. Often, audit questions will lead to another question as the auditor follows the audit trail trying to get to the ultimate evidence that a requirement is being met.

Auditor Notes

Auditors need to be able to take good notes during the audit. This helps them recall the details of the audit when preparing the audit report. Notes need to record the evidence the auditor observed during the audit. This can be evidence of conformity or not.  Being able to show what the auditor saw or heard during the audit is an important part of the audit process. Good note taking skills are one of the competencies auditors need to possess and continually develop.   

Preparing EHS Compliance Audit Findings 

Auditor notes are the evidence of conformity, but sometimes the audit shows things are not the way they are supposed to be.  Auditors call these nonconformance’s, or potential noncompliance findings. There are many formats for preparing these negative findings. One approach is to write the negative finding in three parts:

1. the requirement,
2. the finding and
3. the evidence that supports the finding

The requirement part of the finding describes the audit criteria the auditor was trying to prove true.  It can be a regulatory requirement or a requirement the organization has set for itself.  The finding part is a statement of what the problem was, and often refers to the requirements. The evidence part of the audit finding is a summary of what an auditor saw that led them to the conclusion there was a nonconformity.   

The following is an example of a negative finding for potential noncompliance with a State issued Title V air emission permit. 

  • Requirement: [s. NR 439.055(2)(a), Wis. Adm. Code, 02-DCF-178] The pressure drop across the dust collector baghouse shall be measured and recorded once every 8 hours of operation or once per day, whichever yields more measurements.  
  • Finding:  Auditee not able to produce records of baghouse pressure drop readings
  • Evidence: No records of metal finishing baghouse pressure drop were able to be produced for 2nd & 3rd shift when baghouse was operating in May 2023. 

Communicating EHS Compliance Audit Findings

When a negative finding is made auditors should try to get consensus with auditee that the finding is valid. This will help avoid disagreement on the validity of a finding during the closing meeting. This also helps confirm the auditee has a clear understanding of what was wrong so they begin to fix the problem. Well written findings also help auditees identify appropriate corrective actions. A correction is a quick fix to “stop the bleeding”. A corrective action prevents the nonconformity from recurring.  

Closing Meeting

A closing meeting should be held for all EHS audits. During the closing meeting the audit team shares the results of the audit with the auditee. The closing meeting should include the following:

  • Audit findings
  • Audit conclusions
  • Audit recommendations (if appropriate)
  • Circumstances that affected confidence in the audit results
  • Audit report timing and distribution
  • Follow-up actions to be taken by the auditors and auditee
  • Process for appealing an audit finding or conclusion

Conclusion

This is Part 2 of a three-part article about environmental and health and safety (EHS) auditing. Part 1 discussed how to plan an EHS audit. In Part 3 of this series we will explore how to follow-up on an audit including preparing an audit report, approving corrective actions and verifying corrective action effectiveness during subsequent audits. 

ECSI provides auditing, consulting and training services to organizations interested in improving their EH&S performance. For more information, contact us.

Pro-Tips for Best EHS Audits (Part 1): Planning An EHS Compliance Audit

Introduction

Environmental Health and Safety (EHS) audits help organizations confirm that EHS risk is being managed to an acceptable level.  Processes for conducting EHS audits continue to evolve.  This three-part article will explore why and how EHS audits are performed.  The techniques are based on principles of auditing that have been used for many decades by financial accountants.  These techniques are now being adapted to audits of EHS performance.  EHS audits assess EHS regulatory compliance, management systems conformance and other important areas of EHS performance. This part of the three-part series explores best practices for planning effective EHS audits.

Part 1 – Planning an EHS Audit

Planning an EHS audit starts with understanding the purpose and objective of the audit.  Auditors need to understand who is requesting the audit (the audit client) and what the audit results will be used for.  This information helps auditors define the scope of the audit and what resources will be needed to achieve the audit objective.  Documenting and sharing the audit objective and scope early in the audit planning process helps ensure there is agreement between the auditor and the auditee.  Figure 1 is an example of how an auditor might document the audit Objective and Scope as part of developing and EHS audit plan.

Audit Objective and Scope statement in an audit plan

Figure 1 – Audit Objective and Scope statement in an audit plan

Determining EHS Audit Duration

With the objective and scope confirmed, an auditor can determine how much time will be required to perform the audit (audit duration). This includes estimating time to plan the audit, collect audit evidence, review the evidence and prepare a report of the audit findings and conclusions.  Sometimes the auditor needs to conduct a preliminary Stage 1 audit to help judge auditee readiness, gather additional information to determine the audit duration and confirm the audit is feasible. Differences between the duration proposed by the auditor and what the audit client is willing to pay, need to be resolved before the audit begins. Changing the scope of the audit can often help the auditor and auditee reach consensus on the duration of the audit.

Auditor Competence

The confidence that can be placed in the results of the audit are directly proportional to the auditors competence. Auditor competence includes knowledge of the regulatory requirements (the audit criteria) and the processes that are the subject of the audit. Audit team members should also have developed audit skills including, how to conduct interviews, how to follow audit trails and how to record audit evidence.  Auditor behaviors are also critical including maintaining confidentially and making the auditee feel at easy during the audit.

Preparing an EHS Audit Schedule

With the audit duration established competent auditors can now develop and document a plan to conduct the active evidence gathering part of the audit.  The plan should identify where the auditor plans to audit, when they plan to be there and what evidence they will be evaluating.  It can also include who the auditors intend to interview during the audit.  This helps the auditee schedule meetings with the auditor and avoid delays in the audit due to interviewee being unavailable when the auditor desires to conduct the interview.   

Confirming the Audit Schedule

Once the audit plan is established it should be shared with the audit client and the auditee to ensure agreement on when, where, and how the audit will be conducted.  When agreement is reached the auditor can begin to make plans for travel and accommodations during the onsite portion of the audit.  Figure 2 is an example audit schedule for a hypothetical metal parts manufacturing facility that also has an electroplating process.

Example EHS Compliance Audit Plan

Figure 2 – Example EHS Compliance Audit Plan

Summary

In this part of the 3-part compliance audit series we explored how to plan an EHS audit.  In Part 2 of the series, we will explore how to conduct an EHS audit by following audit trails and recording audit evidence.  In part 3 we will explore processes for reporting and following up on the results of an EHS audit.

ECSI provides auditing, consulting and training services to organizations interested in improving their EH&S performance. For more information, contact us.

This is the first of a three-part article that describes best practices for planning, conducting, and following up on environmental and occupational health and safety regulatory compliance audits.

This three-part series we will consider best practices for:

  • Part 1 – Planning audits
  • Part 2 – Conducting audits
  • Part 3 – Following up on audit results

ISO 45001 Webinar – FREE!

ISO 45001 is an international standard that helps organizations improve Occupational Health and Safety (OHS) performance.  The ISO 45001 standard can be used to ensure workers are safe by protecting them from workplace injury and ill health.  As the Vice Chair of the US Technical Advisory Group to ISO 45001, I have been seeing a significant rise in awareness of ISO 45001 benefits.  Environmental Compliance Systems, Inc has also helped many organizations plan, implement and integrate an ISO 45001 OHSMS with their other business management systems.   A recent webinar produced with ASSP describes the many benefits of an ISO 45001 OHSMS.  Here is a link to free ASSP webinar: https://player.vimeo.com/video/844292169?. Please watch if you are interested in improving your organizations OHS performance.

Definition of Risk in the ISO High Level Structure

ISO 45001:2018, 14001:2015 and 9001:2015 are based on the High Level Structure. The International Organizations for Standardization (ISO) High Level Structure (HLS) is about to enter another phase of revision of the HLS. The definition of “Risk” in the ISO HLS and the term “risk and opportunity” is causing confusion with drafters and users of ISO 45001.

Removing the special definition of term risk and eliminating use of the term risk and opportunity will help standards drafters reduce ambiguity in the standard requirements and help other users better understand how to plan. implement, operate and audits ISO management systems.. The following discussion is based on our extensive experience auditing, teaching and consulting for ISO 45001, 14001 and 9001.

The Definition of “Risk” and Use of the Term “Risk and Opportunity” in ISO High Level Structure

The HLS was introduced in 2012 to “harmonize” management system standards around a common structure. The common structure helps organizations integrate quality, environmental, health and safety and other management systems.

ISO HLS TOC

Figure 1 is the Table of Contents of the HLS as currently proposed in Draft ISO/DGuide 83 – 06/03/2020.

In this post we discuss two issues being raised during the HLS revision process.

These are:

  1. the definition of the term risk in the HLS,
  2. use of the terms risk and opportunity in the HLS.

Resolving these two issues is important to users understanding of what ISO 45001 is designed to manage.

In a previous post, we provided an overview of proposed changes to the HLS duirng the minor revision stage, As the HLS revision begins to enter the major revision stage we believe there are important issues to be addressed by ISO. We believe that ISO should carefully consider the unintended negative consequences of creating a special definition of risk and using the term risk and opportunity in future versions of the HLS.

Risk as a “defined term”.

Definition of risk

The Oxford English Dictionary (OED) is the official dictionary of ISO and defines risk as the “possibility of loss, injury, or other adverse or unwelcome circumstance”.  The Merriam-Webster definition is similar, “possibility of injury or ill health”. These definitions of risk have been in use for many decades and with great success by organizations managing Occupational Health & Safety (OH&S) performance.

In 2012 ISO introduced the term risk as a “defined term” giving it a different definition than OED or Merriam -Websters. The HLS definition of risk is now “the effect of uncertainty” (see Figure 2).  

Definition of Risk

The new definition is designed to encourage organizations to take a broader view of both the positive and negative characteristics of risk. This approach is supported by the ISO technical committee that develops guidance standards on risk management (TC 262). ISO 31000 is the flagship standard in this series. ISO 31010 is guidance on risk assessment techniques.

Use of “on objectives” in the HLS definition of risk

TC 262 isnow promoting another revision to the definition of risk that adds the words “on objectives” to the HLS definition of risk They believe the concept of risk cannot be comprehended without reference to the term objectives in the definition of risk (Figure 3).

31001 definition of risk

However, adding the words “on objectives” creates ambiguity and confuse drafters and users of ISO 45001. This is because the term objectives is already used in 45001 referring to specific goals the organization needs to achieve to improve OH&S performance.

The objectives refereed to in the ISO 31000 definition of risk are more broad and include business and societal objectives. The potential unintended consequence of adding the words on objectives to the definition of risk is users will only address risk associated with objectives and not more broadly address OH&S risk to workers and the organization..

Unintended consequences of changing the definition of risk

The addition of a special definition of risk has increased ambiguity about the meaning of the term risk. It has also had unintended consequences for both those using the HLS when developing management system standards, and those using these standard to plan and implement OH&S management systems..

As an example, because of the way ISO has now defined risk, the developers of ISO 45001 found it necessary to add two additional notes to the definition of risk (Figure 4). The ISO 45001 definition of risk now has 6 notes (198 words) to explain the three word definition of term risk.

ISO 45001 Definition of risk

The drafters of ISO 45001 also found it necessary to create another defined term OH&S risk (Figure 5). This new definition was added to clarify ambiguity caused by the HLS definition of risk and how OH&S professionals had traditionally understood the concept of risk in the OH&S management discipline.

Definition of OH&S Risk

The intent of the new ISO special definition of risk was to shed light on the practice of risk management and encourage organizations to take a broader view of the dynamics between risk and opportunity. That objective may have been achieved but with significant additional confusion by standards drafters and users. ISO should consider removing the special definition of risk from the HLS and return to use of the Oxford English Dictionary of risk.

Risk and Opportunity in the High Level Structure.

The association of the word risk with the word opportunity (risk and opportunity) in HLS clause 6 has confused drafters and users of ISO 45001.  There is uncertainty if the term risk and opportunity refers to a single concept or two different concepts. To help explain what is meant by risk and opportunity ISO prepared a white paper titled Risk Based Thinking in ISO 9001:2015. Although the title indicates the topic is ISO 9001 Quality Management systems, the examples used in the white paper are also applicable to an ISO 45001.

To clarify ambiguity about the term risk and opportunity, drafters of ISO 45001 added a new defined term OH&S opportunity (Figure 6).

Definition ofOH&S Opportunity

The ISO 45001 definition of OH&S opportunity refers the concept of OH&S performance improvement, another defined term in ISO 45001 (Figure 7) . The definition of OH&S performance references another 5 defined terms in ISO 45001. The need to create a separate defined term of OH&S opportunity and then refer to 5 other defined terms to explain the OH&S performance, This tortured effort to reduce ambiguity is further evidence of the confusion the term risk and opportunity has introduced to ISO 45001.

Definition of OH&S Performance

ISO 45001 also refers to other risks and other opportunities that the organizations needs to address (Figure 8). These terms are not defined in ISO 45001. This adds uncertainty about the concept of risk and opportunity in ISO 45001.

Figure 8 – ISO 45001 Other Risk and Other Opportunities

These many terms associated with the concept of risk and opportunity in Clause 6 creates uncertainty about what ISO 45001 is supposed to manage.  Those implementing, operating and auditing an OHSMS are confused, especially when identifying what is important to the organization’s OH&S performance.  The unintended consequence of adding the term risk and opportunity is user confusion about answers to important questions like:

  • When the HLS uses the term opportunities is it referring to potential financial or societal gain or to a discipline specific intended result such as a safer workplace?
  • What is the difference between the concept of risks and opportunities and the concept of OH&S risk, OH&S opportunity and other risk and other opportunity or are these the same thing?
  • Are the concepts of hazards and risks being tre focus of OH&S management systems now obsolete, or can it still be used when planning an OH&S management system?

Conclusion and Recommendation

The introduction of a special definition of risk and the use of the term risk and opportunity in the HLS has led to unintended and unnecessary confusion by drafters and users of ISO 45001. ISO should remove the definition of risk and use of the term risk and opportunity from the ISO HLS. during the next phase of the HLS revision.

WDNR Green Tier – Internal Audits and Corrective Action

WDNR Green Tier Internal Audits

The WDNR Green Tier program requires participants to conduct periodic “outside” EMS audits to check that the system is functionally equivalent to ISO 14001:2015.  By law, the minimum frequency of these audits is once every three years for Tier 1 participants and annually for Tier 2 participants. 

Many organizations choose to perform WDNR Green Tier audits more frequently than prescribed by the Green Tier law.  Longer than a year between audits result in increased risk to the organization.  Postponing an annual physical from your doctor increases the risk that a medical condition will becoming a bigger medical issue.

WDNR Green Tier audits also provide important information to leadership.  Reviewing Green Tier audit findings during management reviews allows leadership to evaluate how the EMS is functioning and if it is achieving the intended results. Leadership may miss important information when it reviews the results of audits only every three years.

Organizations that invest in their WDNR Green Tier audit program have better performing EMS’s and get a better return on their EMS investment.  ISO 19011:2018, Guidelines for auditing management systems provides guidance for organizations wishing to improve their EMS audits.  This guidance includes:

  • How to establish audit programs
  • How to conduct audits and report audit results
  • What competencies auditors need to possess
  • How to evaluate auditor competence.

Using the results of WDNR Green Tier Audits

WDNR Green Tier EMS audits evaluate audit criteria against audit evidence. Performing WDNR Green Tier audits ensures that “what should be is” and “what should not be is not”.  Examples of audit criteria are requirements of Green Tier functional equivalence, compliance obligations such as permit requirements or requirements such as WDNR universal waste and hazardous waste regulations.  They can also be internal requirements the organization has set for itself.

A robust EMS audit process and procedures coupled with effective corrective action process to address audit findings is critical to the effectiveness of am EMS.  If the audit process or the corrective action process is weak the EMS may not be able to achieve the intended results of the EMS.

WDNR Green Tier Audit Corrective Actions

Green Tier audits are fundamental to superior environmental performance, but audits alone do not make changes that improve performance.  Audits simply identify conformance and nonconformance to the requirements of Green Tier and the organizations internal requirement for the EMS. 

Audits can be good news or bad news.   If an organization is performing audits and find nothing but “good news” that is not especially noteworthy to leadership.  Things are going along well, according to plan, and there is no identified need for action. When audits find nonconformances or bad news, this is good news to leadership because the audit has identified things that need to be fixed.  

If organizations are either not performing effective audits or no audits at all this is bad news for leadership.  Leadership has no way of knowing if the EMS is performing as planned.  “No news” is bad news.

Audit nonconformance findings are good news and a source of EMS performance improvement.  Audit nonconformances are not evidence of failure or reason to find fault. Doing so will create fear of the audit process within the organizations and increase the difficulty in gaining employees trust and cooperation with the audit process.

To benefit from the results of audits organizations also need to fix the nonconformance problems the audits discover. Performing audits and then being unable to correct the problems discovered is often a bigger problem than not performing audits at all.  An example is an audit of regulatory compliance status that discovers a potential noncompliance.  Uncorrected findings later discovered in a regulatory agency compliance audit could result in enhanced “knowing and willful” criminal penalties.  Finding a potential noncompliance problem and not fixing it is worse than not finding it in the first place. To reduce risk, organizations need to take corrective action on audit findings in a timely fashion.

Some organizations struggle to get traction on their corrective action process for two primary reason.

  • A clear process or workflow for performing corrective action has not been defined and or communicated by the organization.
  • The organization has not established a systematic way to keep track of and report on if and how the nonconformance are being addressed.

WDNR Green Tier Audit Corrective Action Workflows

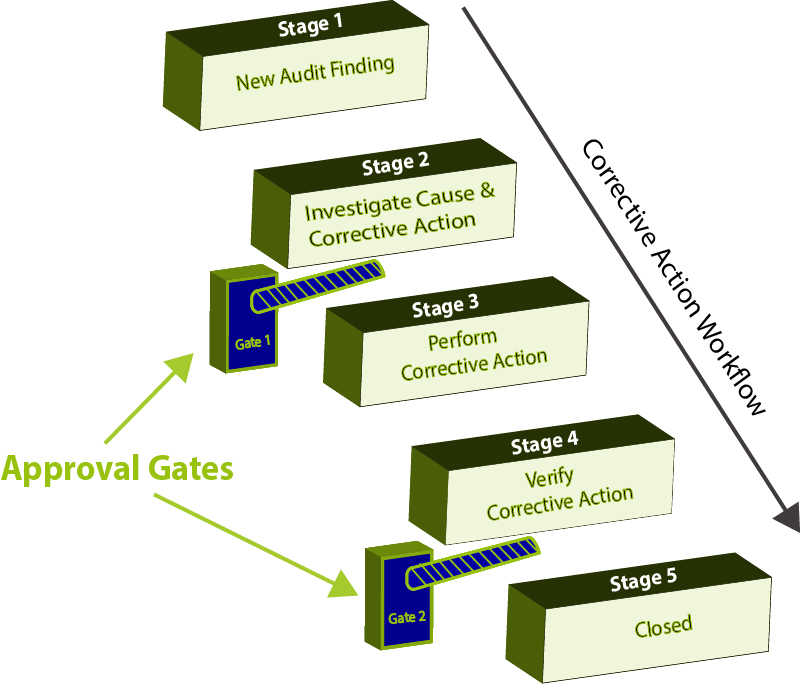
Corrective action workflows for audit nonconformance should be a team effort.  Teams should follow several sequential steps collaboratively and reach consensus on each stage in the workflow. The last stage of the workflow is verification of effectiveness of the corrective action.

This team approach is similar to the collaborative product design process used by industries to develop products. The design process has desecrate points in the process called gates. Design teams agree that each step was completed before the design process can progress through the gate to the next stage

The purpose of this design review workflow is to ensure the design process is proceeding in a systematic fashion and to minimize the potential for design flaws that will become apparent in the production or use stage of product or service.

Figure 1 is an example of a corrective action workflow with approval gates and stages.

Corrective Action Workflow with QApproval Gates
Corrective Action Workflow with Approval Gates

Gates separate some of the stages in the corrective action workflow.  The number of approval-gates in the corrective action process can vary depending on the organizations’ needs.  Stages in the corrective action workflow can include:

Stage 1 – New (Contain and Assign)

Recognition of the problem is the first step in the corrective action workflow. Recognition can occur as the result of an audit or incident.  How the workflow proceeds after recognition depends on the gravity of the problem or incident encountered.   The team leader or gate keeper needs to quickly decide what type of problem it is such as:

  • Easy to Fix – We understand the problem cause and we can just fix it because it is unlikely to recur
  • Not so easy to fix – We do not fully understand the problem but believe that the cause and solution can be discovered without commitment of substantial resources at this stage.
  • Difficult to fix – This type of problem needs significant resource (horsepower) to address it with skill. 

The preliminary evaluation will determine the size and competencies of the team needed to address the problem.

The team should consider Immediate steps to contain the problem (stop the bleeding) and what that containment should be.  Placing lables and dates on the universal waste containers corrects the audit finding.The person assigned to the corrective action task should not delay implementation.

Stage 2 – Investigate (Cause and Corrective Action)

Cause analysis

Putting a band aid on the problem with a short-term correction alone will not address the underlying problem cause and the nonconformance is likely to recur.   Determining the cause of a problem is necessary to find a solution that fixes the problem and prevents recurrence.  The team should investigate why the problem happened in the first place. 

Root cause analysis is a huge topic and there are many approaches to doing a cause analysis, but sometimes asking “why did that happen?” several times can help identify the underlying cause of the problem (5 why analysis).  Other problems can be more complex and require more horsepower than a 5 why analysis can deliver.  These types of problems may need more sophisticated cause analysis techniques such as Six Sigma (DMAIC), 8 Disciplines (8D) or others.

Corrective Actions

The root cause of the problem helps the team discover an effective corrective action that will prevent the problem from recurring. The team should reach consensus that the proposed corrective action is appropriate to the cause before the corrective action is implemented. This will improve the likelihood that the corrective action will fix the problem in a way that it will not happen again..   

Corrective action solutions that are based on one individual’s perception of the root cause and how to fix that problem often oversimplify both the cause and the solution.  The tendency is for individuals to hurry the process and close the nonconformance as quickly as possible.  This leads to weak root cause analysis which in turn compromises the selection of an appropriate corrective action. 

If the corrective action process is not monitored in a team setting the assignee is more likely to close out the issue (get it off their desk) as soon as possible.  A team approach to the corrective action process that use approval-gates can help avoid this consequence. Approval-gates encourage robust cause analysis.  

The following is an example of poor cause analysis and proposed corrective action for the audit finding that universal waste containers were not properly labeled and dated.

  • Proposed Cause –  “The employee had not been trained in how to properly package and label the universal waste”. 
  • Proposed Corrective Action:  Train the employee in how to properly package and label universal waste. 

This cause analysis simply repeats the finding.  It does not describe why the problem happened in the first place and the proposed corrective action is more of a correction than a corrective action.  Implementing this action will not ensure that the same problem does not happen again.

Root Cause Analysis

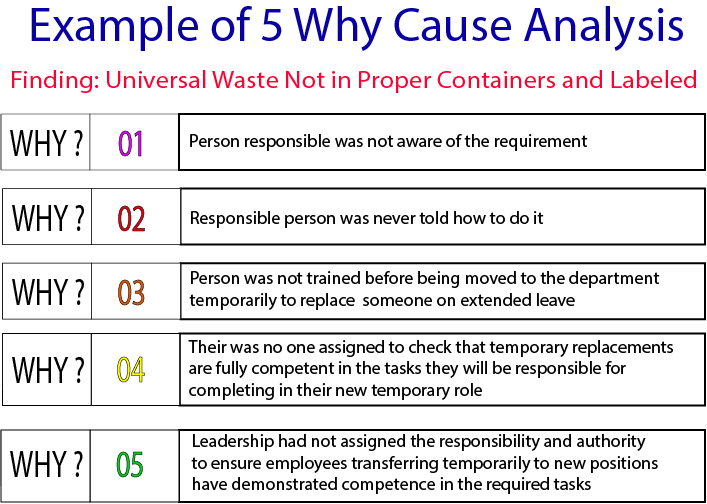
Figure 2 shows the results of a more appropriate cause analysis of the universal waste packaging and labeling nonconformance.

Example of 5 Why Cause Analysis
5 WHY Analysis

Once the root cause is identified an appropriate corrective action can be proposed that will prevent it from happening again.

Often there are several options for corrective actions that fix the problem in a way that it does not recur.  Some might have potential to be extremely effective but are costly to implement.  An example might be to outsource the universal waste management to a contractor that comes to the site daily to check that the universal waste is being management correctly.  This is highly effective and can transfer some of the risk of universal waste management, but it is expensive to implement.  Before the corrective action is approved the team needs to decide if the proposed corrective action is appropriate for the cause.

An appropriate corrective action decided by the team for this problem and cause might be something like:

  • Leadership will direct the HR department to develop a training matrix that shows competence required for all jobs including temporary fill in positions.
  • The HR department will develop a process(es) that require(s) employees to demonstrate competence to do a job before the employee can be assigned to that job including temporary fill-in positions.

The team should reach consensus that the proposed corrective action is appropriate for the root cause before it is implemented.  Once approved the actions should be implemented without delay.

Stage 3 – Perform (Corrective Action Implementation)

The team implements the corrective action after it is approved by the team and its leadership.  One individual can implement a simple corrective action quickly. Complex problem solutions may require development of a project plan that assigns team members tasks. Task assignee’s need to accomplished these task by established dates. The team monitors progress on the tasks and periodically reports to the team leaders.

Stage 4 – Verification of Effectiveness

Verification confirms that the agreed upon corrective action was implemented as planned.  It also confirms that the corrective action implemented was effective and fixed the problem in a way that it will not happen again. 

Corrective action verification is usually performed by internal or external auditors during regularly scheduled or other audits.  Others in the organization or on the team can perform the verification but it is important that the verifier be independent to the implementation process or the area where the verification is occurring. 

Stage 5 – Closed

Team can close the corrective action after it has been verified. The team may need to invest additional effort if the verification finds that the corrective action implemented did not fix the problem. The team may need to re-investigate the cause and to re-propose and implement another corrective action.

Communicating and Tracking Corrective Action Status 

A significant stumbling block that organizations sometime encounter when addressing nonconformances is the absence of a method to communicate and track the status of completion of the corrective action.  Information about corrective action status has traditionally been paper based or electronic.  These systems assign a corrective action task to someone to investigate and complete. 

The team leader passes the physical or electronic copy of the corrective form to team member responsible for investigating the cause and proposing a corrective action.  Then the paper or electronic copy is passed to other team members to add information or it is returned to the team leader for review and approval.   

Assignee’s can misplace paper or electronic copies of corrective actions.   Paper-based tracking systems require large three ring binders to store the completed corrective action forms and associated supporting documentation such as pictures or other evidence of completion of the corrective action.  Electronic documents are often individually stored in folders located on the organizations servers or in the cloud.

With paper-based systems, communicating the overall status of corrective actions to leadership requires a labor-intensive process of thumbing through the three ring binders and manually recording the status of the corrective actions.  Individual documents stored on servers or in the cloud have similar problems.  Sorting through individual folders and files takes time to to find important information about the corrective action program.   Use of electronic spreadsheets can help here but create other problems that limit the effectiveness of this solution

Corrective Action Tracking Database Apps

Industry 4.0 revolution will soon fundamentally and significantly change almost all business. This revolution is helping organizations store data optimize equipment and operations using the cloud environment.   Organizations will be able to access enormous amounts of information with a click.  Affordable cloud-based applications that track corrective action progress progress of are now becoming available to all types of businesses. Some of these application are easy to use and allow quick access to trends that inform management decisions.

The heart of these cloud based applications are databases that organize and store information.  They help communicate the status of corrective actions to team members and leadership.  These applications make it easy to monitor the approval-gate process and communicate with team members via automated emailing functions when the status of a corrective action changes or is approaching a due date.  Correcttrack.com is a cloud based application that helps organizations keep track of Green Tier audit findings and improve the effectiveness of the corrective action process.

Conclusion

WDNR requires Green Tier participants to periodically audit their Green Tier EMS.   Audits confirm the organization has established and is operating a “Functionally Equivalent” EMS that results in superior environmental performance.  They are the critical “checking” part of an effective functionally equivalent EMS.  If performed with skill the audit results can provide important information that the organizations leaders need to determine if the EMS is achieving its intended results. 

Ensuring the results of audits are addressed in a timely fashion is critical to an effective EMS.  This is especially true for nonconformance and noncompliance audit findings because findings that go unaddressed or with poor corrective actions increase the risk to organizations than if audits had not been done at all.